Browsing Tag
Malware
2367 posts
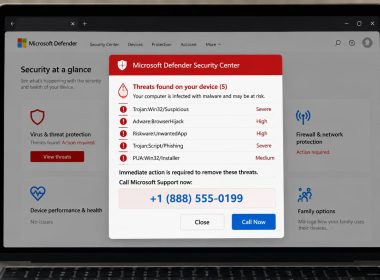
Tech Support Scam Kit Uses Google Ads to Deliver Fake Security Alerts
Google Ads deliver a tech support scam kit that shows fake security alerts, makes browsers appear locked and…
SectopRAT Abuses Legitimate Audio Software Files to Steal PC Data
FortiGuard found SectopRAT hidden in modified audio software files, using staged loading to steal browser data and remotely control infected Windows PCs.
New AvisLoader Windows Malware Uses ClickFix Lure and Tox P2P for C2
Varonis Threat Labs discovered AvisLoader, a Windows malware loader that uses the Tox peer-to-peer network for C2 and arrives through a malicious ClickFix lure.
RatHat Android Malware Uses AI to Target Banking Credentials in Real Time
RatHat Android malware uses generative AI to navigate infected devices, steal banking credentials, intercept OTP codes and reinstall itself after removal again.
MovieReaper Malware Uses The Odyssey Torrents to Infect Users Worldwide
MovieReaper malware spreads through compromised Odyssey torrents, infecting hundreds of victims while using Solana to locate command-and-control infrastructure.
New TASK#STOMP Windows Backdoor Enables Continuous Document Theft
TASK#STOMP Windows backdoor uses PowerShell, scheduled tasks and runtime C# compilation to steal business documents and maintain remote access.
China-Linked FamousSparrow Deploys SparroWocky Backdoor in Latin America
FamousSparrow is targeting Latin American governments with SparroWocky, a new C++ backdoor that exfiltrates files, takes screenshots and evades security tools.
ClickFix Attacks Spread ChainScript RAT via Fake Spotify and Teams Installers
Blackpoint Cyber found ChainScript, a Node.js RAT spread through fake Spotify, Zoom and Teams installers that uses Polygon smart contracts to locate its C2 server.
CrowdStrike Links AI-Generated PhantomRaven Malware to Bug Bounty Hunter
CrowdStrike links PhantomRaven malware to a bug bounty hunter, finding LLM-generated code, malicious npm packages and attempts to compromise company IT systems.
Ukrainian Conti Ransomware Member Gets Four Years in US Prison
Ukrainian national Oleksii Lytvynenko gets four years in US prison for his role in the Conti ransomware operation, which targeted over 1,000 victims.